
A team of agents that ships secure code with you.
Shield finds vulnerabilities across your mobile apps, web apps, and the code in your editor, then proves each one with a working exploit. Inside your perimeter.
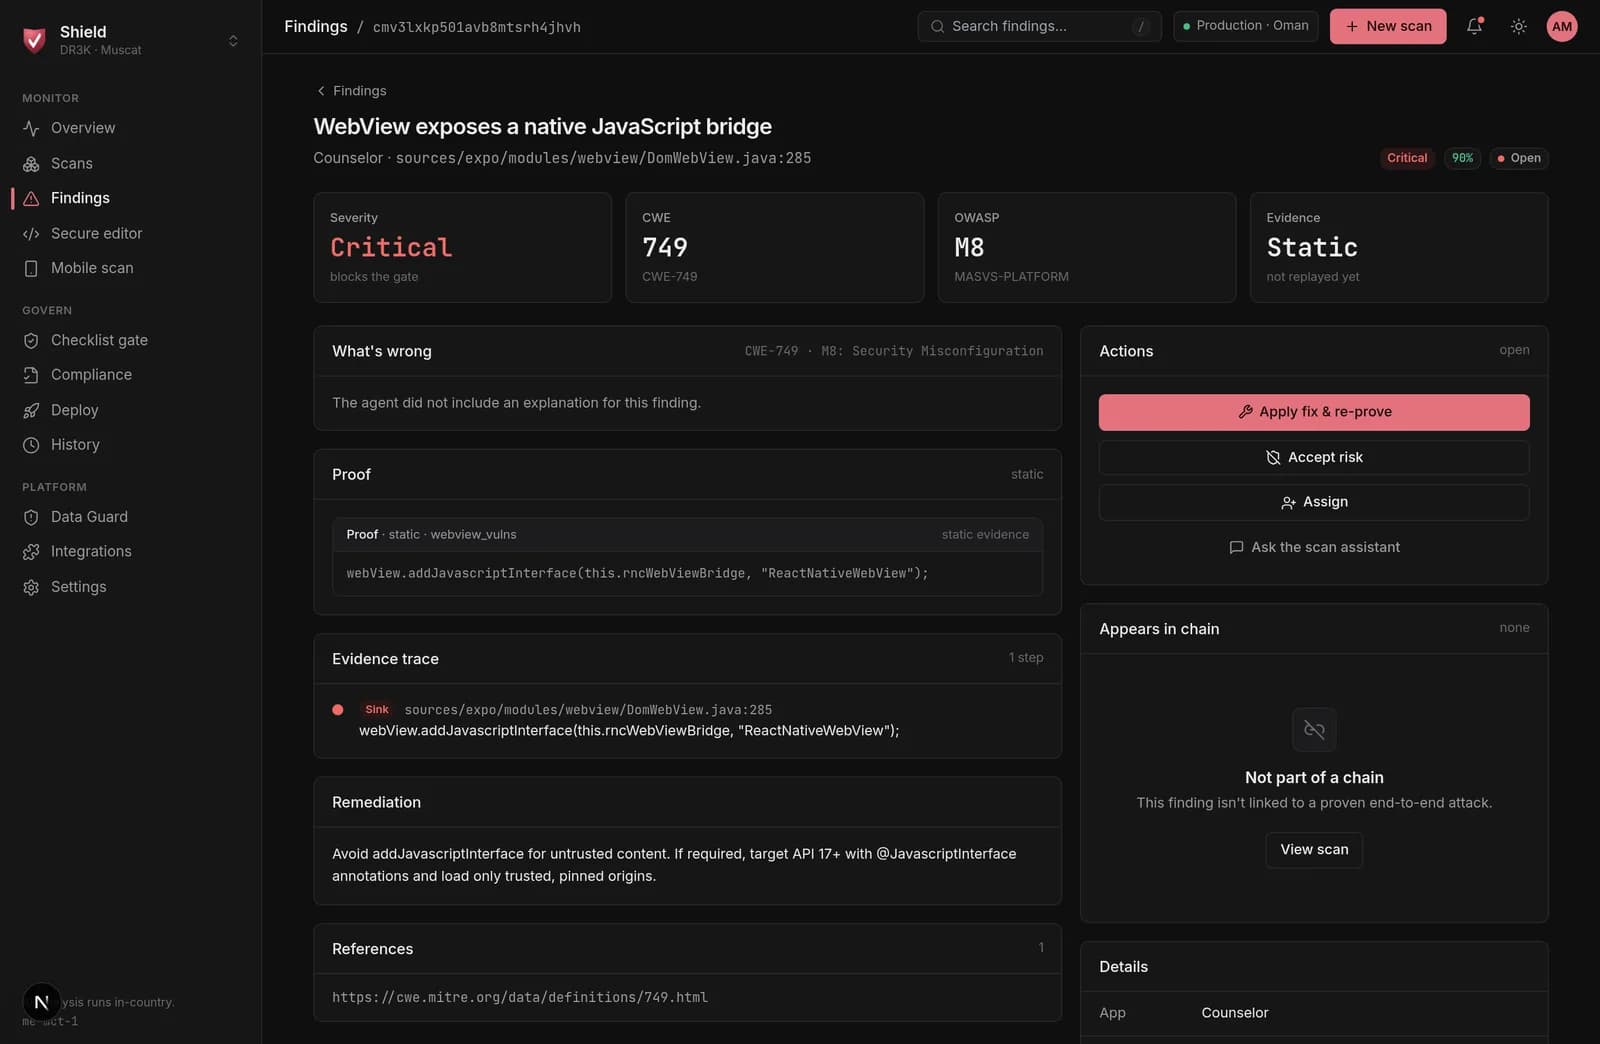
Tests across the stack your team ships
Security work that ends in proof.
Scanners stop at a severity score. Shield keeps going: it reproduces the finding, captures the evidence, and keeps it inside your perimeter.
Proven, not flagged
Every finding is reproduced against the running target before it reaches you.
Inside your perimeter
Shield deploys where the code lives; model calls stay in-country by default.
One pipeline, every surface
Mobile, web, and the editor run through the same agents and evidence model.
Mapped to your auditors
Each finding carries evidence aligned to the frameworks your auditors apply.
Reproducible audit
Every scan replays from intake to report, long after it was found.
Held to its own standard
Single-tenant, encrypted, and logged end to end. The way it asks you to build.
From discovery to a proven exploit, in one run.
A target moves through four stages without leaving your environment. Nothing is flagged on a hunch. It is reproduced or it is dropped.
Discover
Agents read your code, crawl your apps, and map every surface an attacker could reach.
Prove
Each exploit is reproduced against the running target, with the request, response, and state it reached.
Report
A short list of proven findings, each with a working exploit and an audit trail your team can act on.
Govern
Every scan carries a chain of custody, mapped to the frameworks your auditors use, gated before release.
Walk the console, stage by stage.
The same run, from discovery to governance. Each view is the real Shield console, not a diagram.
Map every surface first.
Agents read the code and crawl the running app, building one model of everything an attacker could reach. Before a single test is written.
- Static read of native, managed, and config
- Authenticated crawl of apps and APIs
- One normalized model, shared downstream
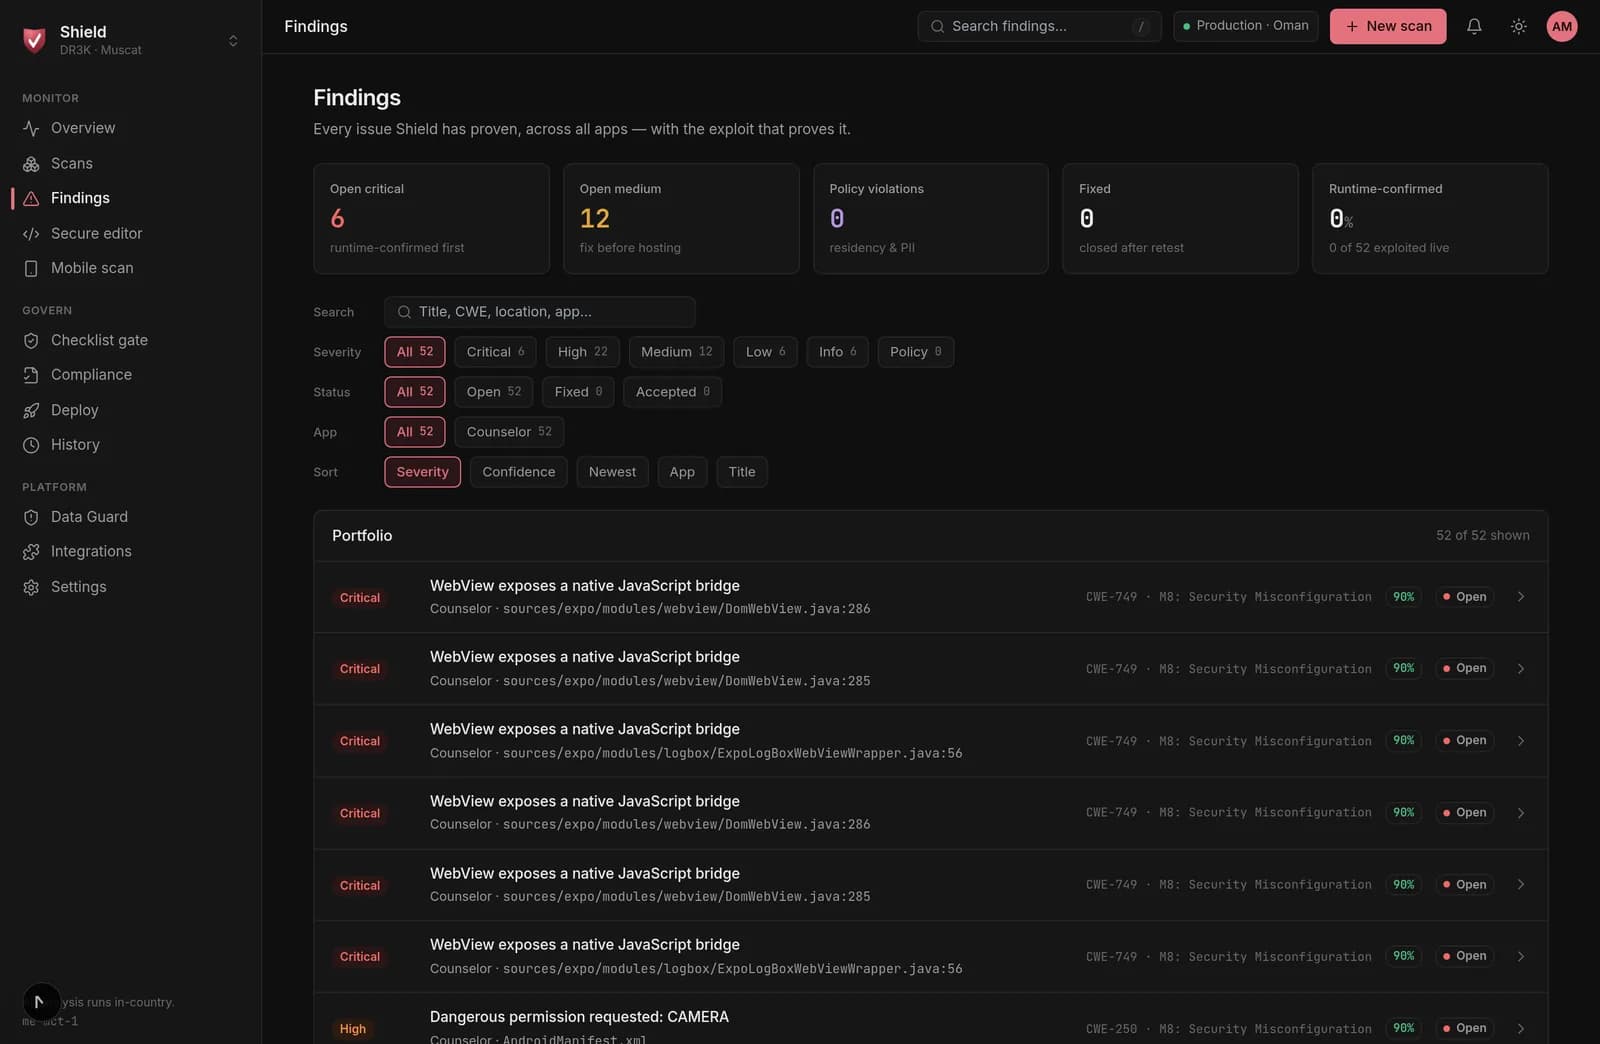
Every finding has already been proven before you read it.
Inside your perimeter. By default.
Built for teams that answer to a regulator.
Where the code cannot leave the country and a finding has to stand up to an auditor.
Banking
National banks and payment rails.
Government
Ministries and public infrastructure.
Fintech
Regulated startups moving fast.
Telecom
Carriers and critical networks.
A short list of proof, not a backlog of maybes.
Without Shield
A scanner's output
- A backlog of maybes to triage
- Severity scores, not proof
- Findings you still have to reproduce
- Code sent off to a vendor
With Shield
A proven short list
- Findings already reproduced
- A working exploit for each one
- Evidence mapped to your frameworks
- Everything inside your perimeter
Questions teams ask first.
Do you store our code?
No. Shield deploys inside your perimeter; your code and model calls stay in-country by default, and every outbound decision is logged.
What counts as a finding?
Only a reproduced one. Proven against the running target, with the request, response, and state captured.
Which surfaces are covered?
Mobile apps, web apps and APIs, and the code in your editor. All through one pipeline and one evidence model.
How do we start?
Request a pilot on a single surface. We stand Shield up inside your environment and show you the first proven findings.
See Shield run on your own code.
Pick a surface you ship. We will show you the findings, each one already proven.